suresecure on the road 2021
suresecure on the road in 2021
Here is an overview of all the events we attended in 2021. It was all virtual, but we still had the feeling that we were out and about.
DER SECURITY HORST -
DER SECURITY HORST -
We launched our podcast in May 2021 and are proud to already have over 2,000 downloads. Our podcast deals with relevant topics relating to IT security in the business environment.
The Security Horst provides new insights into the world of information technology and its security every month: security incidents following cyber attacks, securing IT infrastructures, the use of SIEM and SOC, and much more... Stay up to date and keep going!
Insider Research in conversation...
Insider Research in conversation...
... with Jona Ridderskamp about the impact of digitalisation on IT security. ENISA advises an incident response management plan - we explain the best way to proceed.
Source: security-insider.de
Webinar it-daily.net
Webinar it-daily.net
A SIEM can be used to collect all messages and log files from various systems. But how do you make the collected data usable in real life? The simple answer: by correlating data records. But what exactly is behind this answer: which data records should be correlated, which systems should be connected and how do you decide which events are important and which are not? On 16 June, Jona Ridderskamp spoke about the topic "Carpe SIEM - Use your logs".
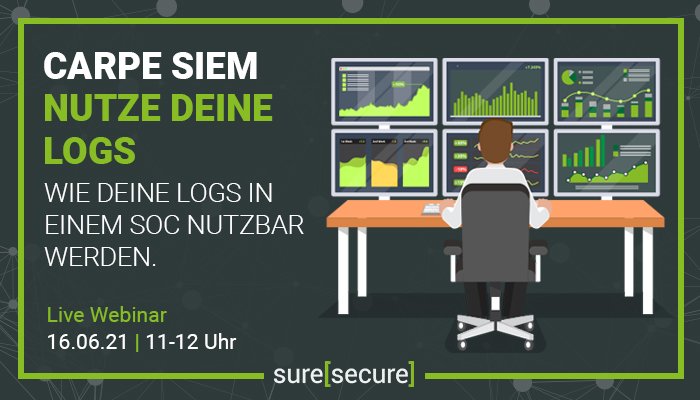
Own presentation
Webinar Handelsblatt
Webinar Handelsblatt
The number of cyber attacks is not only continuing to increase, it has now reached an alarming high. Data has become a very lucrative currency that cyber criminals are trying to tap into using various forms and methods of attack. Criminal hacker gangs are now operating professionally and offer their services "as a service" on the darknet. It is therefore more important than ever to firmly anchor IT security in the corporate strategy.
Andreas Papadaniil spoke about this topic on 6 July 2021. Here is the link to the article.
Recovery from a security incident can range from days to weeks to millions of euros!
Internet Security Days 2021
Internet Security Days 2021
On 16./17.09.2021 Thomas Günther spoke at the Internet Security Days on the topic: IT security concept - hot or junk? An IT security concept is indispensable for establishing IT security in a company and making it "tangible". Read the summary of the presentation on our blog to find out how best to proceed when creating an IT security concept and which technical and organisational measures need to be defined.

Own illustration
4. Annual Cybersecurity Conference
4th Annual Cybersecurity Conference
Convent's 4th Annual Cybersecurity Conference took place on 28 October 2021. Thomas Günther explained WHY an IT security concept is necessary at all, WHY you should adhere to certain standards when developing it and WHY it still needs to be customised for each company.
In a nutshell, the questions can be answered as follows:
WHY?
An IT security concept is necessary to implement and improve IT security in a company. It is an elementary component of a comprehensive Information Security Management System (ISMS) of a company or public authority. The ISMS can be seen as a strategic tool for IT security. It is a collection of documents and regulations that relate to everything to do with IT and information security in a company, organisation or authority. Basic components are recorded in the ISMS :
Description of the security processes
How to deal with employees (security awareness)
Description of management principles
How to deal with resources
WHAT?
There are certain standards and frameworks for creating an ISMS that you should adhere to:
BSI 200-1: Conceptualisation of an ISMS
BSI 200-2: Definition of three concrete methodologies (core, basic and standard assurance)
BSI 200-3: Risk management and approach to identifying protection needs
ISO 27001: International Standard
These standards are tested, proven and thus serve as a good guideline for the approach to an ISMS.
The responsibility for the topic is clear:
IT security is a matter for the boss
WHY?
Even if the creation of an ISMS always follows the same scheme, the individual areas must be individually checked, implemented and adapted to the respective company.
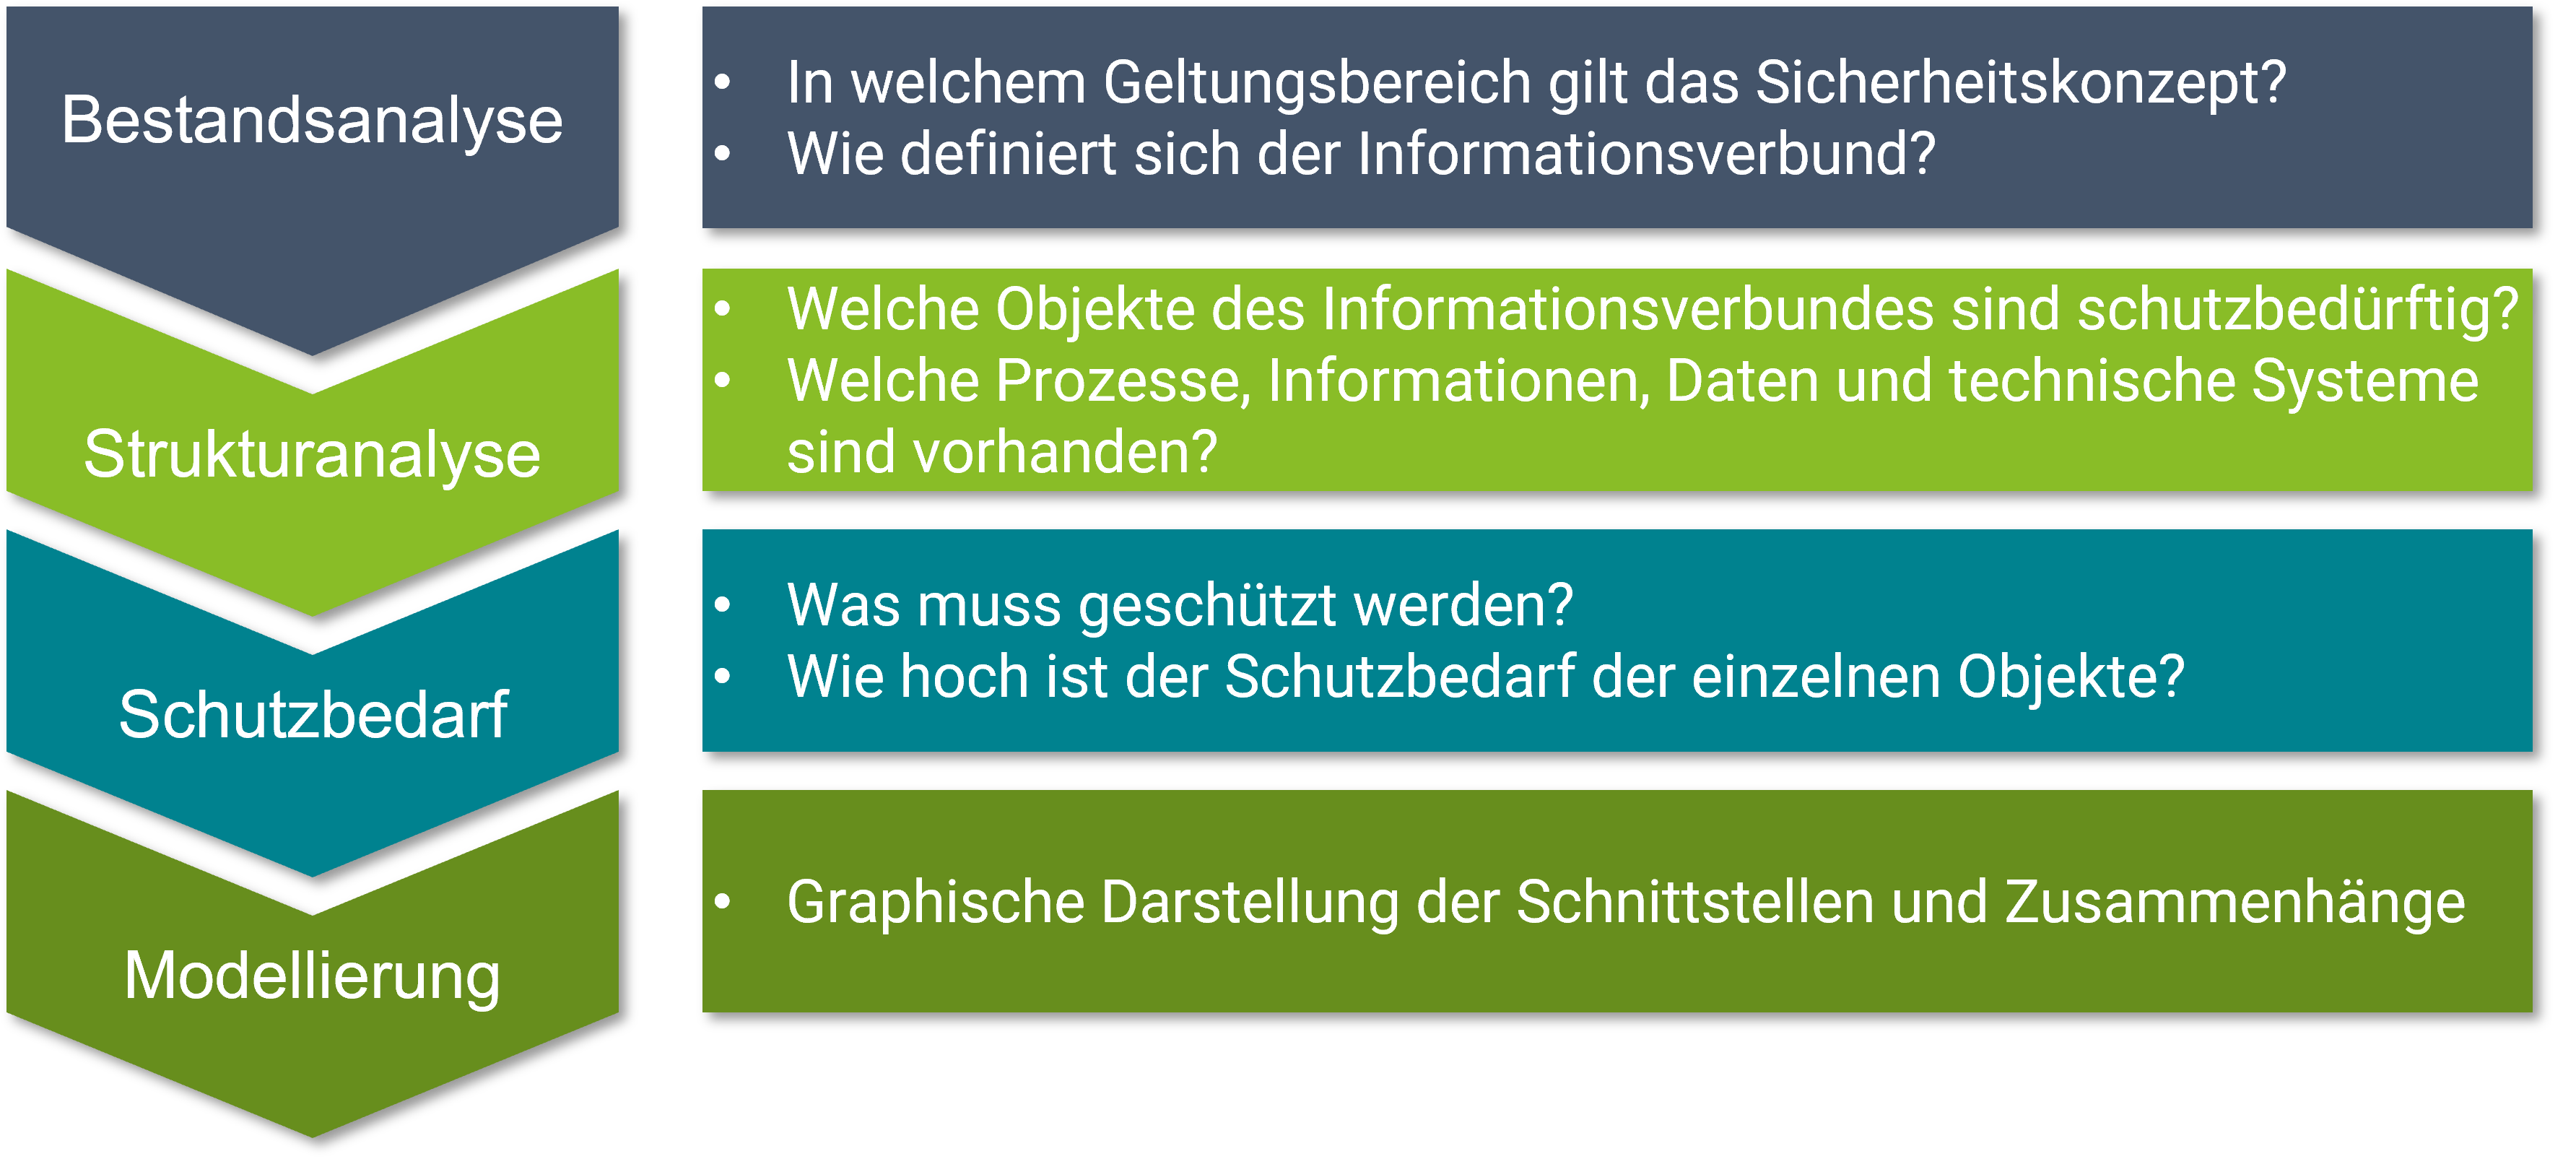
Analysis and process steps in detail, own illustration
IT Security Day
IT Security Day
A good partnership is not only built on trust, but also on balancing weaknesses and promoting strengths. Collaboration between artificial intelligence and humans can be visualised in a similar way. Jona Ridderskamp explained which weaknesses and which strengths are meant here in a presentation at Heise's IT Security Day on 11.11.21.
Artificial intelligence in harmony with human expertise - preventing and dealing with a security incident
Digitalisation is fuel for cybercrime. What does that mean? More digitalisation means more data, more systems and therefore more attack options for black hats. Cybercrime is now a fully-fledged business model with ever new attack patterns. The complexity of attacks is increasing, but the detection rate is falling.
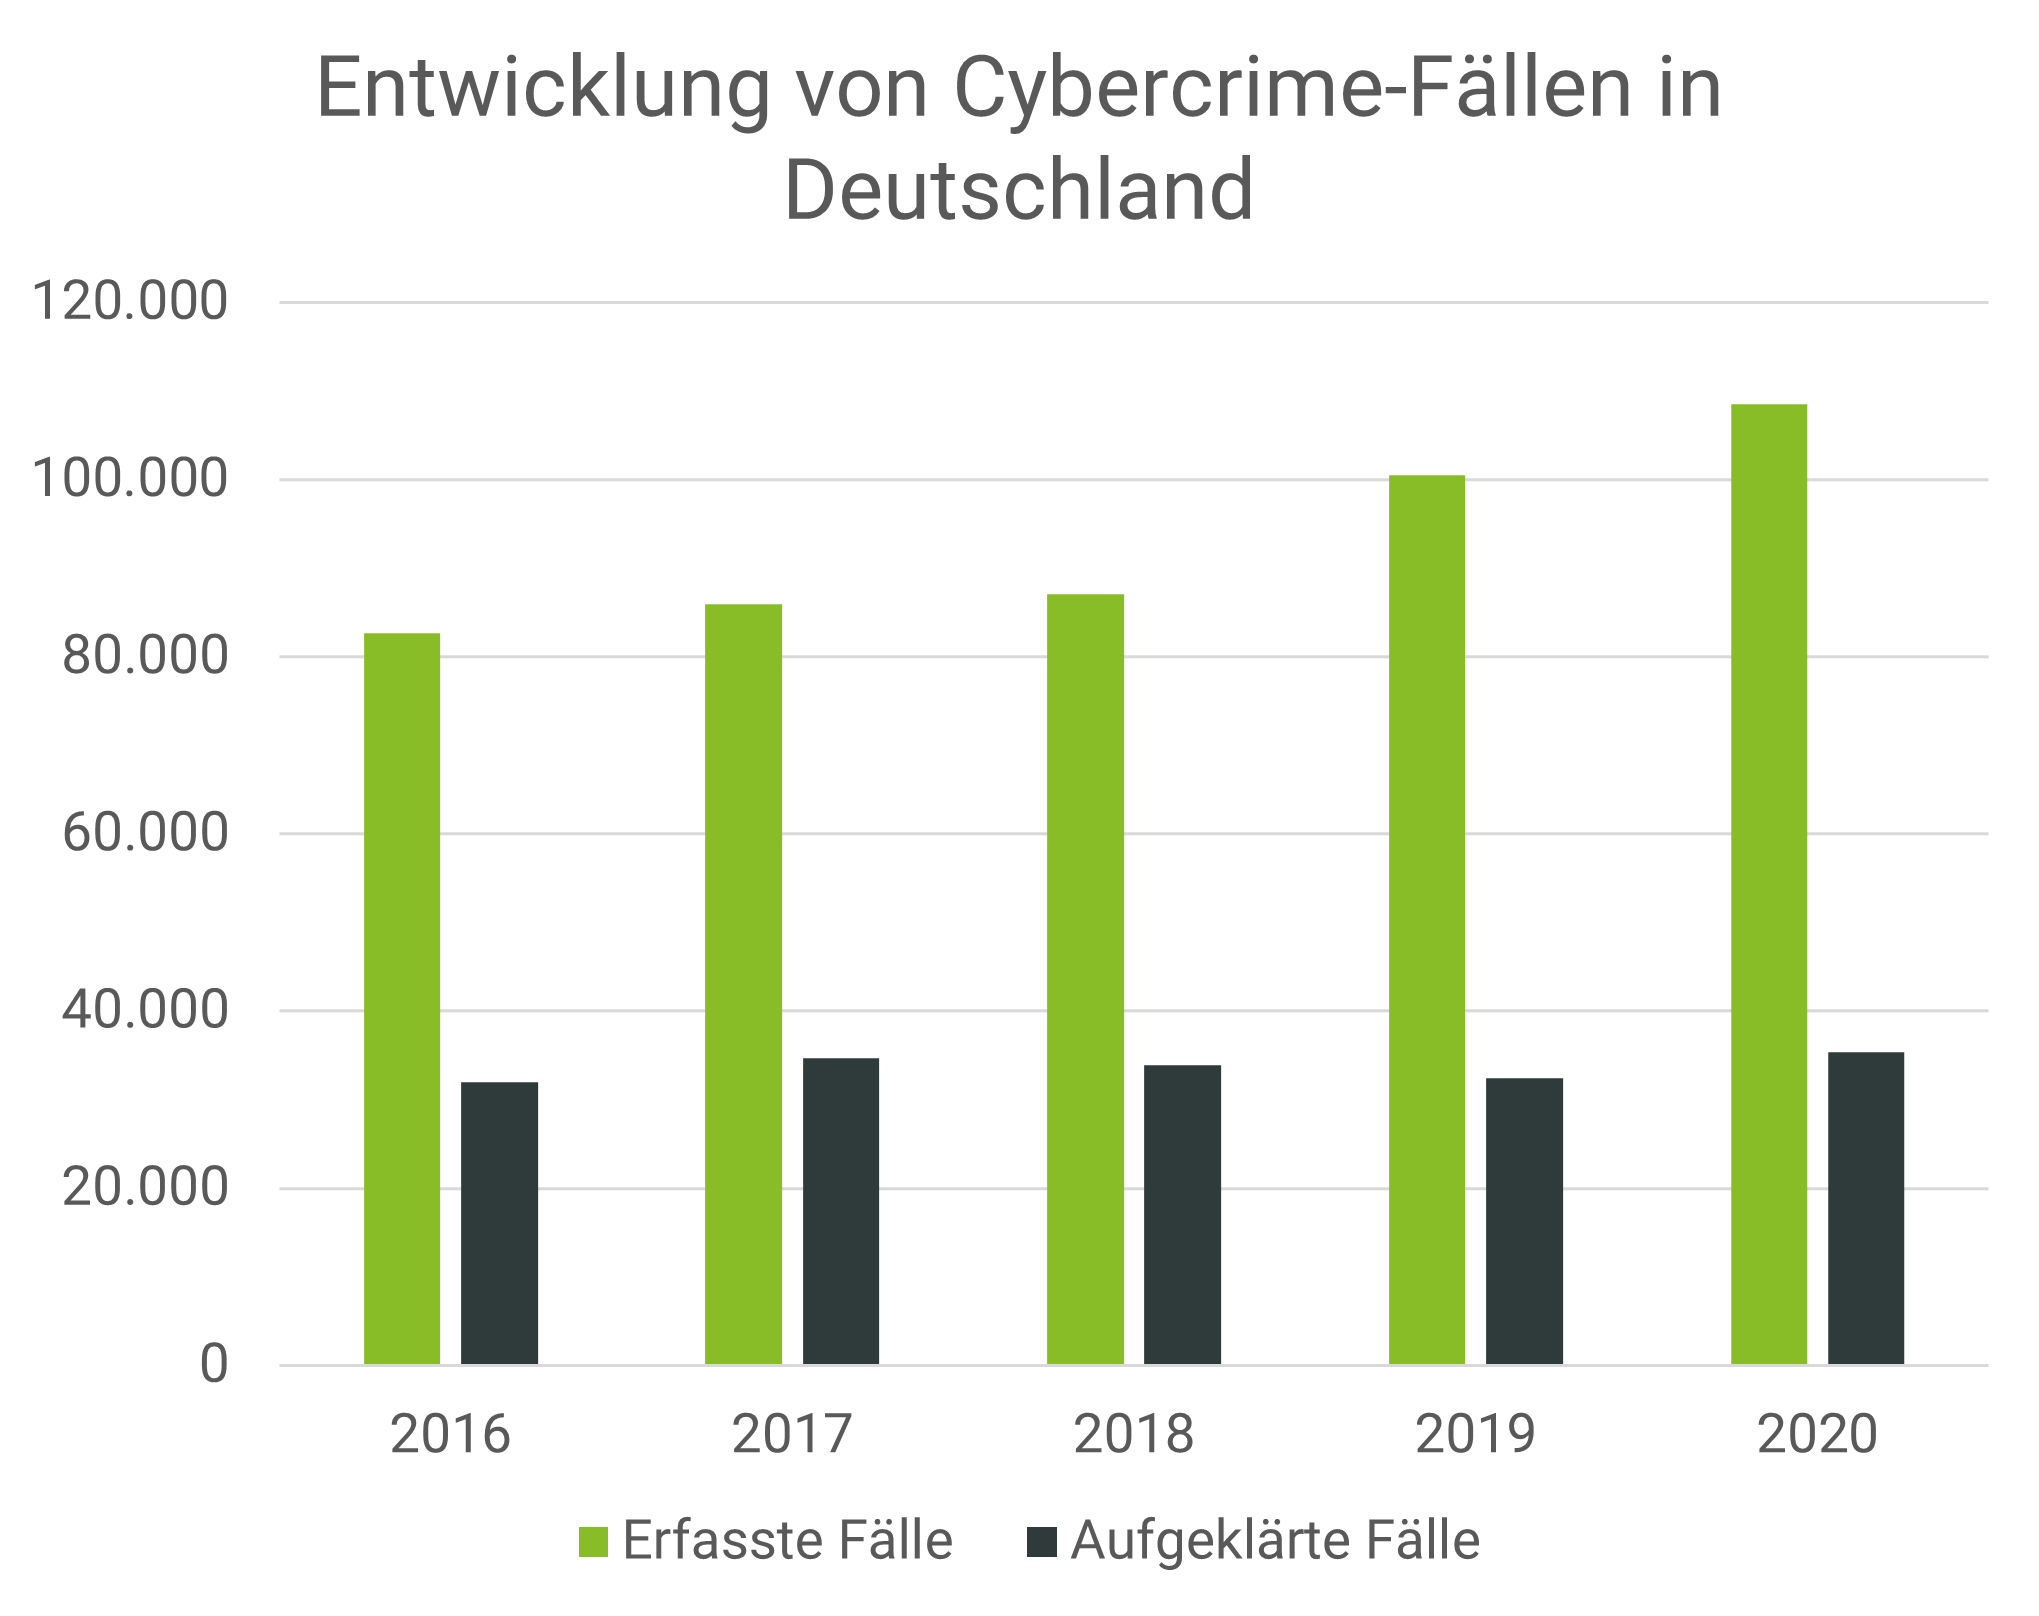
Own image
Automation helps with IT security
Log data, data streams, data exchange and thousands of endpoints. Traffic is increasing enormously and "big data" can no longer be handled manually.
suresesecure 3D Booth
11. Annual Cybersecurity Conference
11th Annual Cybersecurity Conference
The 11th Annual Cybersecurity Conference of Handelsblatt and Euroforum took place on 22 and 23 November 2021. Thomas Günther spoke on the topic
"Cybersecurity in companies - prevention instead of frustration"
Cybercrime is evolving just as rapidly as digitalisation. Sophisticated business models are now behind cybercrime. "Cybercrime as a service", so to speak!
Cyber attacks usually follow the same pattern:
Intrusion into the systems through malware or exploitation of vulnerabilities
Expansion of authorisations
Creation of persistences
Exfiltration of data
Executing the encryption
The attack takes place long before the encryption!
How can you prepare for security incidents?
Concentrate on the essentials
Use, evaluate and understand log sources, e.g. with a Security Operation Centre
Provide sufficient and trained resources - security experts, emergency budget, recovery plan
Incident Response Manager coordinates the incident
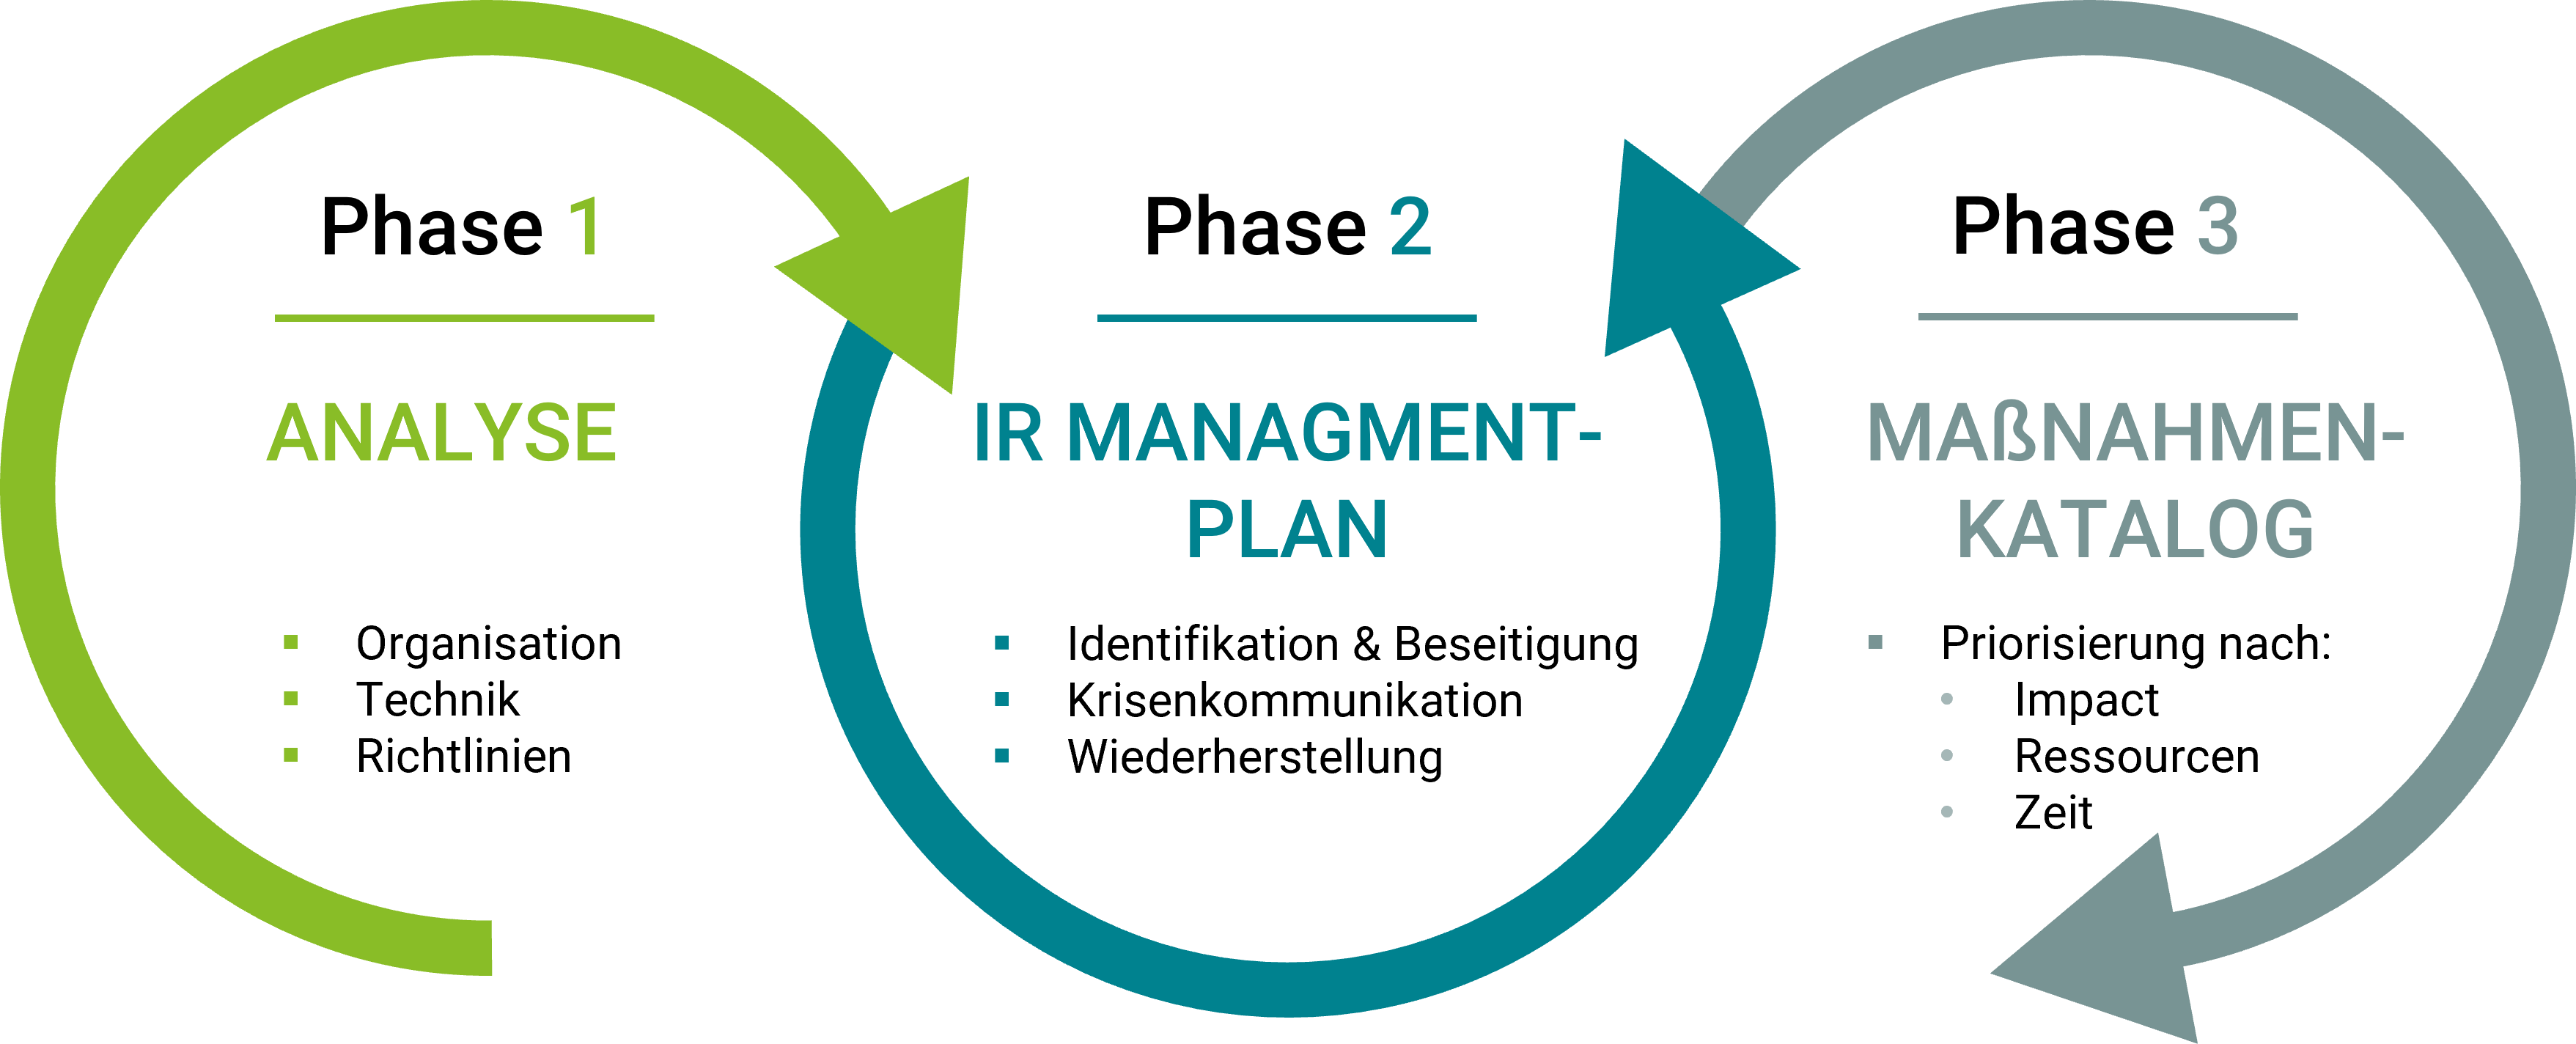
Incident Response Preparation, own illustration
The right preparation is fundamental. No one is 100% safe in the digital world. However, the aim is to detect a potential attack at an early stage to minimise damage.
Cybersecurity webcast
Cybersecurity webcast
On 14 December 2021, a webcast was held on the topic of "Every year again? IT security incidents are no exception for many companies". Moderated by Andreas Horchler, our CEO Jona Ridderskamp answered questions from the participants. We really enjoyed this format and it was very interesting to see what topics were brought up.

Annika Gamerad
Event & Marketing Specialist
Published on 01.01.1970